
Developmental Test and Evaluation: The Discipline That Decides Whether a Program Is Actually Ready
Author

Neerav Singh
Technical Product Specialist
Author
Neerav Singh
Technical Product Specialist
Reading Time
4 min read
Developmental Test and Evaluation: The Discipline That Decides Whether a Program Is Actually Ready
A brake controller program carries 312 verification line items across 4 development builds. Build 3 closes 287 of them. Leadership reads 92% complete, declares the design mature and releases production tooling. Seven weeks later a supplier swaps a connector housing. Someone asks which of the 287 closed items were run on the old housing. Nobody can answer in under 5 days. The program loses a month reconstructing which results still stand and which have to be re-run.
The tests themselves ran correctly. What collapsed was the layer around them: the record of what was tested, on which article, under which revision, against which requirement. That layer has a name in aerospace and defense programs. It is called Developmental Test and Evaluation, and most commercial engineering programs run a version of it without ever calling it that.
What DT&E means
Developmental Test and Evaluation (DT&E) is the disciplined process of generating substantiated knowledge on the capabilities and limitations of systems, subsystems, components, software and materiel, used to inform decisions on programmatic and technical risk throughout the acquisition life cycle. Defense guidance frames it as the deliberate exercising of virtual or real components and the evaluation of responses, applicable from concept through sustainment.
Two words carry the weight. Test produces data. Evaluation converts that data into a defensible statement about readiness. Both are required to get value from a DT&E effort.
Programs rarely fail at the first word. Rigs run. Chambers cycle. Channels record. Failure concentrates in the second word, where results must be tied back to requirements, anomalies chased to root cause and a decision signed by someone whose name goes on it.
DT&E sits ahead of the decision, not behind it
DT&E is one of 3 overarching types of T&E alongside Live Fire Test and Evaluation and Operational Test and Evaluation. It verifies that the design is satisfactory and that technical specifications and contract requirements have been met, and it confirms readiness to move into operational testing. Commercial programs run the same sequence under different vocabulary. Component qualification feeds vehicle-level validation. Vehicle-level validation feeds homologation and customer sign-off.
The distinction that matters for lab operations is timing. DT&E exists to inform a gate decision before the gate closes. A result that lands 3 weeks after tooling release has almost no decision value left in it. Speed of evaluation is a program risk control, and that is a lab operations problem before it is an engineering problem.
Test like you fly
The NASA Engineering and Safety Center report on DDT&E for human-rated spacecraft states the axiom plainly: test like you fly, fly like you test. Tests should replicate actual conditions to the maximum extent possible, covering hardware, software, environments, interfaces and operational sequences. The report argues that testing goes beyond compliance with requirements and can demonstrate that a system accomplishes its intended purpose through mission simulations, end-to-end tests and joint integrated simulations.
Three practices from that report translate directly into commercial physical test labs.
Redundancy must be tested, not assumed.
Every function intended to improve reliability needs verification that it works and that unintended interactions do not defeat its purpose. That requires off-nominal sequences, contingency procedures and negative testing alongside the nominal matrix. Most commercial design verification plans are heavy on nominal coverage and thin on the failure-path coverage that actually protects the product.
Levels of assembly are not interchangeable.
The report is explicit that a lower-level test should not justify omitting a system-level test, and a system-level test should not substitute for lower-level ones. Box-level testing isolates component behavior from external influences, which lets problems surface and get corrected earlier and cheaper. Programs under schedule pressure routinely violate this rule in both directions.
Heritage and COTS parts get the same rigor as new designs.
Existing hardware, reused subsystems and off-the-shelf components carry defects. The report holds that everything in a mission-critical application must be tested with the rigor applied to new designs, regardless of origin. Carryover parts are where verification debt accumulates quietly across model years.
The report also identifies the harder problem: teams have to name the parts of the system that cannot be tested like flight and prove that simulation, analysis or piecewise testing serves as a valid surrogate. That judgment needs to be written down and reviewed, because it is the assumption most likely to be forgotten by the time an anomaly shows up.
The evaluation half
Reviewing results is treated in the report as being as critical as running the test in the first place. Teams must review data, identify adverse trends and recognize precursors to failure. The guidance given to engineers is to listen to what the hardware is telling them.
Unexpected conditions get documented and chased to proximate and root cause. Where cause or corrective action cannot be defined, the discrepancy gets flagged into the risk management process rather than closed out quietly. Test discrepancies whose recurrence would carry safety or mission consequences do not get to sit in an engineer's inbox.
This is where most commercial labs leak the most value. Anomalies get discussed in a review meeting, assigned verbally and never structured into anything searchable. Six months later the same signature appears on a different program and nobody connects the two.
Verification tracking is the spine
The report is direct about tracking. Formal systems should be used to confirm that each requirement is verified against actual hardware and software, and that verification results are peer reviewed.
That single sentence describes work that most programs still run in a spreadsheet. The spreadsheet holds the requirement, the planned test, the sample and the status. It does not hold the calibration state of the rig, the procedure revision in force on the test date, the configuration of the article under test or the approval chain that closed the line. When a connector housing changes, the spreadsheet cannot answer which of 287 closed items are still valid.
Where TITAN fits
TITAN is a Test Lifecycle Management platform built for physical engineering test labs, and it operates at the planning, coordination and traceability layer of a DT&E program. It does not replace DAQ systems or test execution scripting.
DVP management in TITAN holds the verification plan and its outcomes as one continuous record. Every planned test carries its result, the sample it ran on, the conditions applied and the procedure version that governed it. Dependency tracking and progress analysis show the gap between what was planned and what happened without a manual reconciliation cycle.
Configuration context is preserved at the test event. Test article management tracks prototypes and samples from creation through retirement, with test results, incident reports and maintenance history attached to the specific article. A hardware revision change surfaces which results were generated on the superseded configuration instead of triggering a 5 day archaeology exercise.
Scheduling and resource management covers equipment, facilities, personnel and test articles in one calendar view. TITAN flags booking conflicts before they compound and notifies affected stakeholders when a schedule shifts. Levels-of-assembly discipline depends on getting component tests, subsystem tests and system tests sequenced without collision, which is a scheduling problem as much as an engineering one.
Calibration and maintenance state links to test records through asset management, so a result carries the instrument condition that produced it. Automated report generation assembles the evidence package from the underlying records rather than from a re-keyed summary.
Issue tracking gives anomalies a structured home. Discrepancies get logged against the test, the article and the requirement, then carried forward with an owner and a state. Trends become searchable across programs.
Teams running aviation and aerospace certification programs use the same structure to answer certifying-authority requests for the complete test history of a specific hardware article.
The practical takeaway
DT&E discipline comes down to 4 questions a program should be able to answer within an hour of being asked.
- Which requirements currently have verified coverage, and on which hardware configuration.
- Which planned tests have been descoped, and which requirements lost coverage as a result.
- Which anomalies remain open, and what risk each one carries into the next gate.
- Which results are invalidated by the most recent configuration change.
Programs that can answer these make gate decisions on evidence. Programs that cannot make them on optimism and calendar pressure. The difference shows up 9 months later in warranty data, certification delays and the cost of a re-run campaign nobody budgeted for.
A structured test lifecycle management approach turns those 4 questions from a research project into a dashboard query.
Ready to Strengthen Your Test & Evaluation Process?
Bring test planning, configuration tracking and evidence traceability together with TITAN.
Recent Blogs
What Flight Test Management Covers
A certification campaign on a business jet clears 240 test points across 38 sorties. On sortie 22 the instrumentation
Read more...
The Real Cost of an Idle Test Rig
A 4-post hydraulic durability rig carries a replacement value north of $2 million. An environmental chamber rated for combined
Read more...
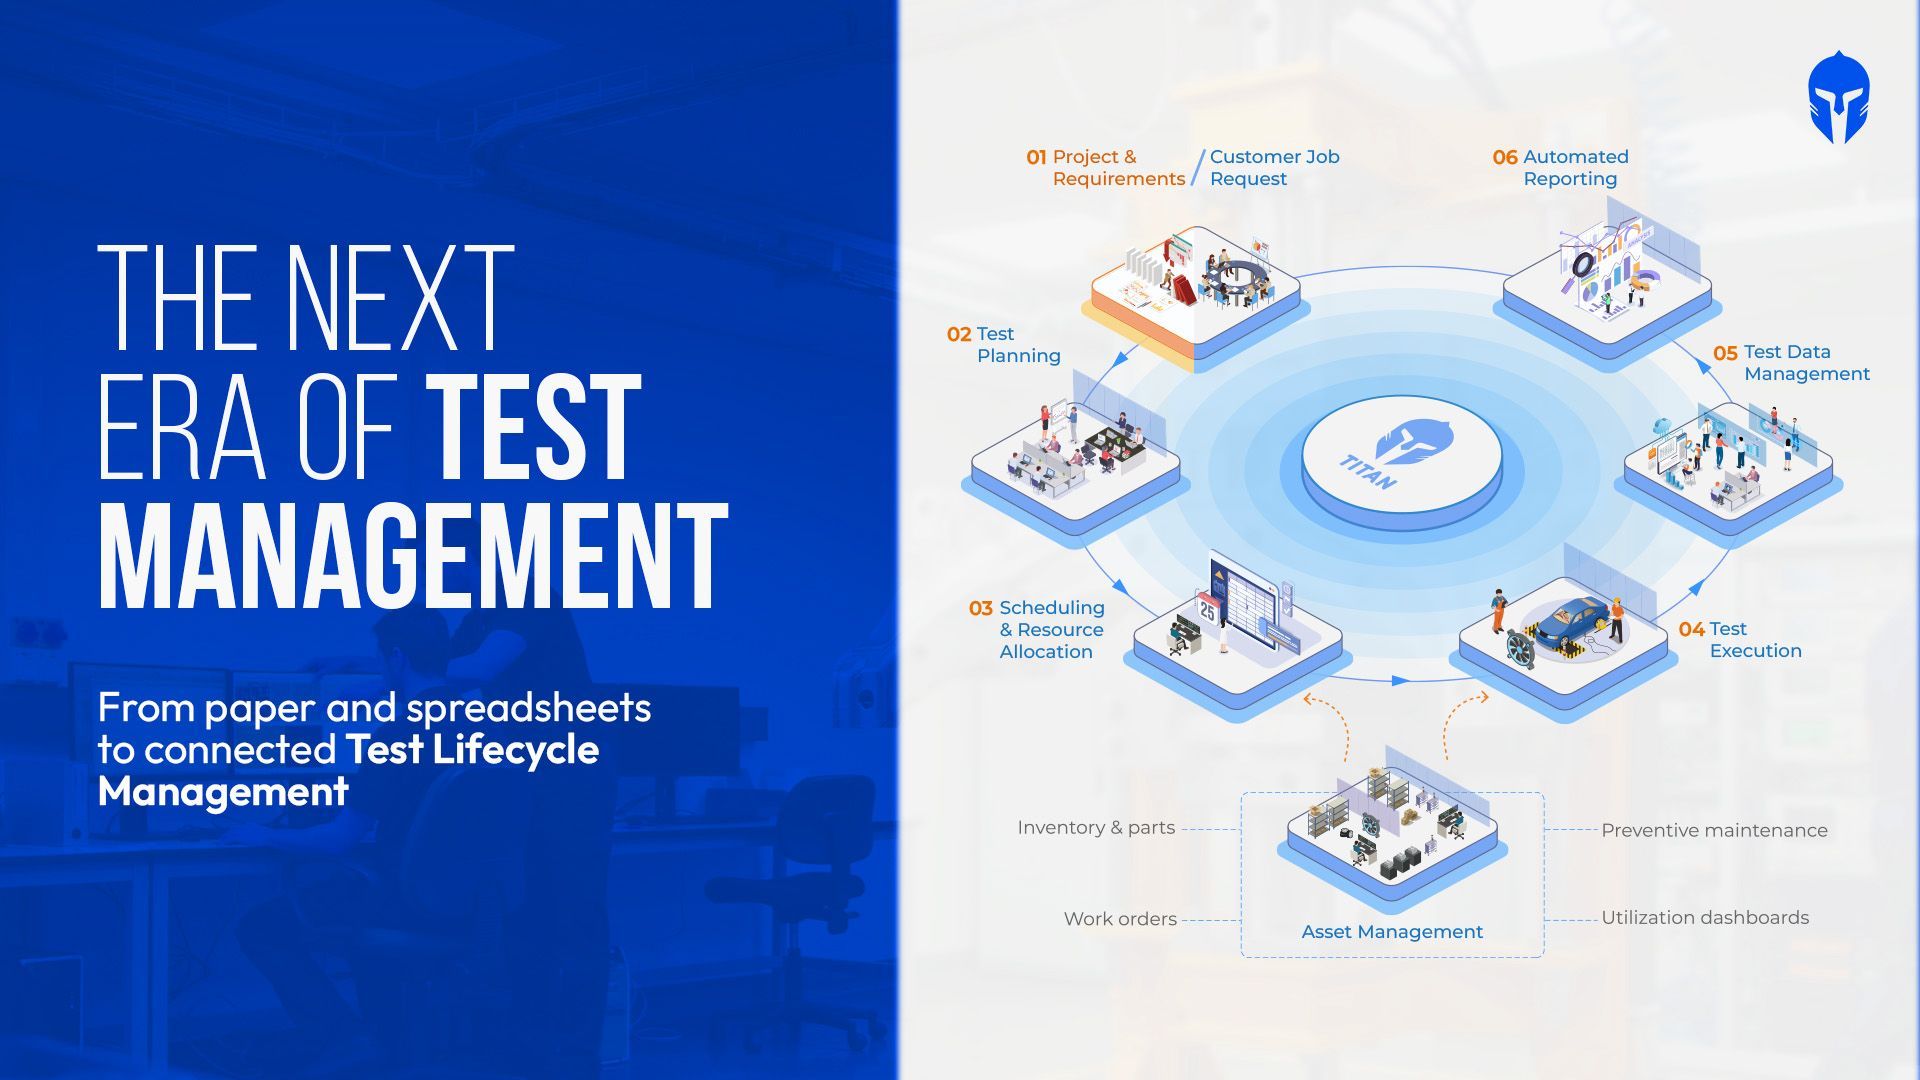
The Evolution of Test Management Tools
Type "test management tools" into a search bar and you get 2 unrelated answers. One set of results covers Jira integrations
Read more...
How to Maintain ISO 17025 Accreditation in Aerospace Testing Labs
It starts with a simple audit question: “Can you show me the calibration record for the equipment used in that test?”
Read more...
Most DVP&R Processes Collapse Before the First Test Even Runs. Here's Why
At some point, the DVP spreadsheet becomes a source of questions instead of answers. Which test count is current?
Read more...
Battery Test Management: How High-Volume Cell, Module and Pack Labs Stay in Control
Weeks into a battery cycle life test, the details start to accumulate: thousands of charge-discharge cycles,
Read more...

What Is a LIMS? A Complete Guide to Laboratory Information Management Systems
Test requests arrive. Samples or test articles need to be identified. Equipment has to be available and calibrated.
Read more...
Vibration Testing Management: From Shaker Scheduling to Test Reports
Every vibration test bay runs on a simple ledger. Hours available on the shaker minus hours testing equals hours lost and eac
Read more...
Euro NCAP 2026: Inside the Operational Challenge for Test Labs
Euro NCAP 2026 puts a different kind of pressure on the test lab calendar. More safety functions need to be validated across more scenarios, with the right vehicles,
Read more...
UAV Testing : Following the Traceability Chain of a Single Aircraft
Somewhere in a UAV qualification programme, a seemingly simple traceability question can become unexpectedly expensive.
Read more...
Faster Automotive Development Starts with Better Test Operations
Modern vehicle programs generate an enormous volume of validation activities, test data, schedules and engineering decisions.
Read more...
How Crash Test Dummies Changed Automotive Safety
In the late 1940s an Air Force flight surgeon named John Stapp noticed a grim pattern. More of his pilots were dying in cars than in planes.
Read more...
Test Management for Component Manufacturers: How to Run Multi-Customer Validation Without Losing Control
Your lab validates parts for more than one customer. Each OEM arrives with its own requirements, its own report format
Read more...
Stop Testing in Isolation: 4 Surprising Lessons from the Ground
Walk into almost any physical test lab and you will find smart people doing careful work inside their own four walls.
Read more...
Why Automotive Testing Labs Need More Than LIMS
When engineers at an automotive testing lab search for software to manage their operations, they often land on LIMS.
Read more...
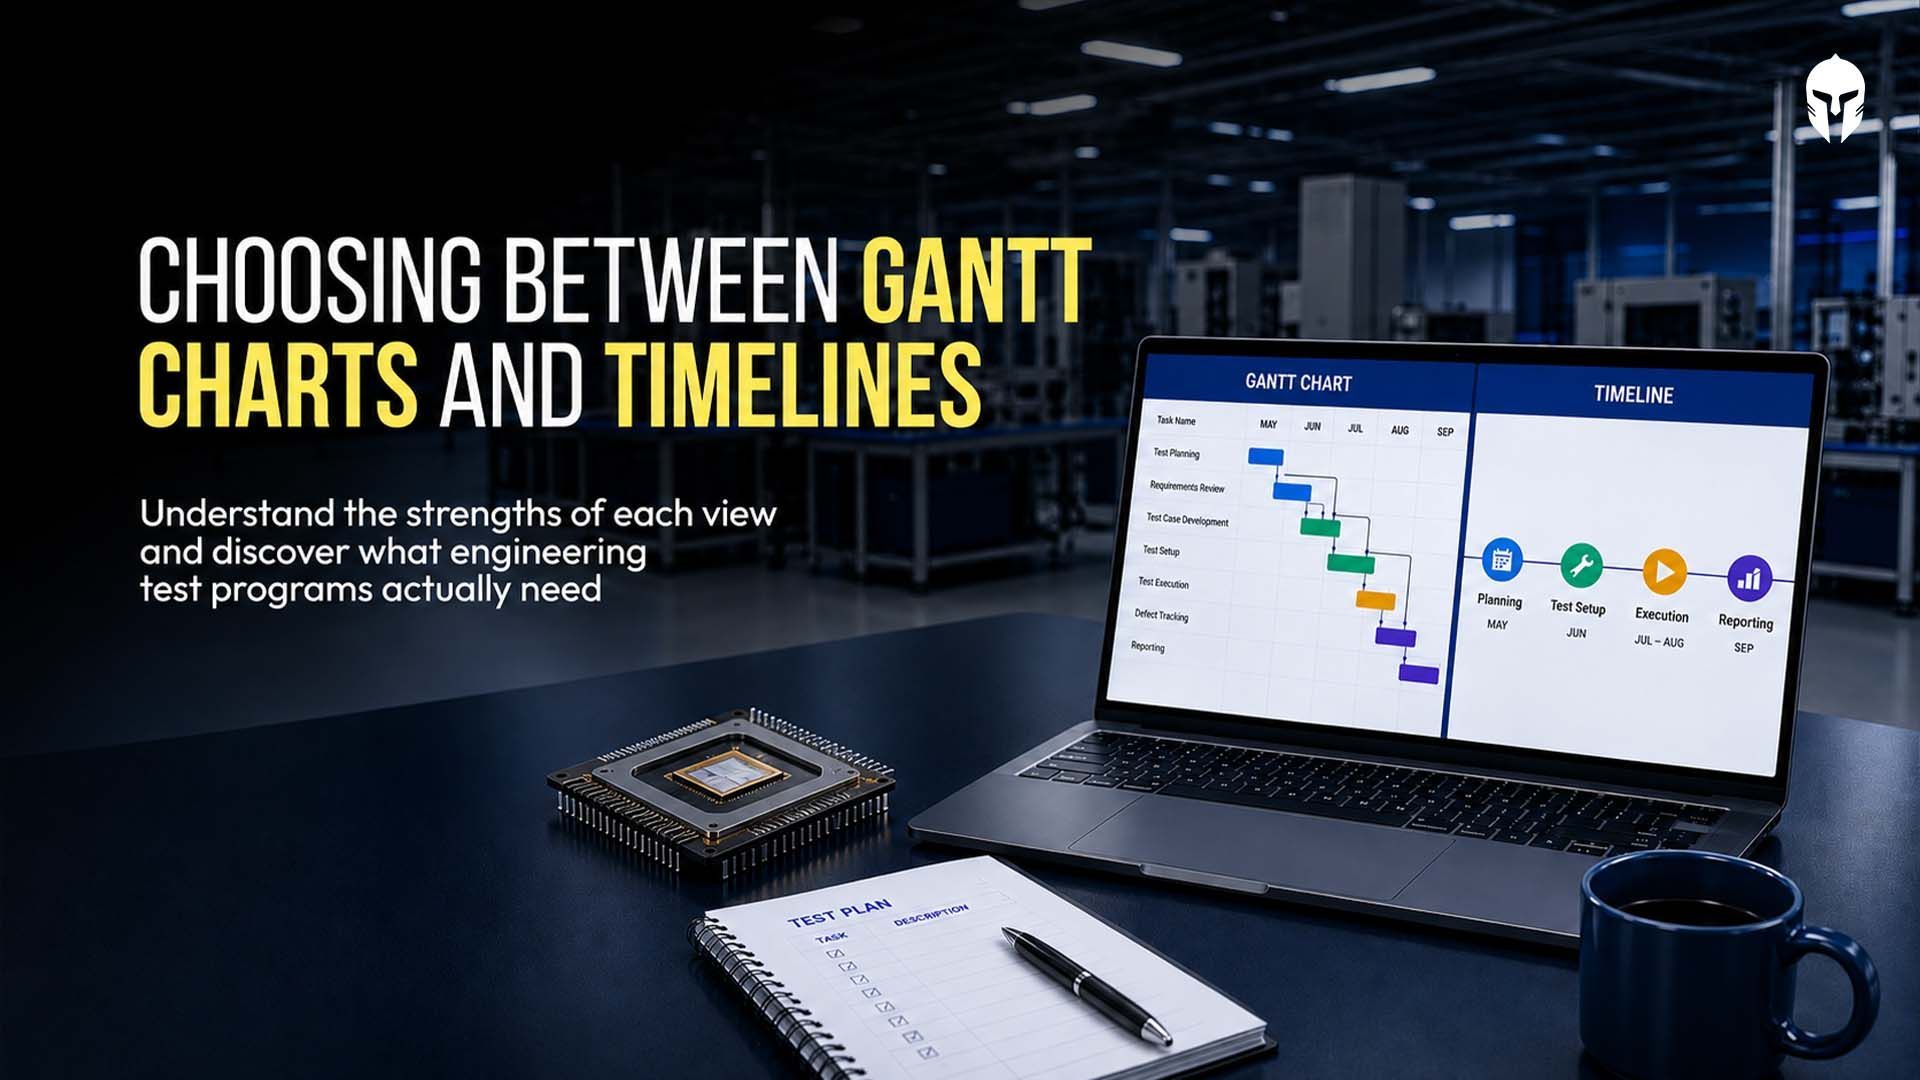
Gantt Chart or Timeline? Picking the Right View for Test Project Management
You open your scheduling tool on a Monday and the program looks healthy. Every test sits inside a neat colored bar
Read more...
7 Critical Problems with Manual Test Tracking in Engineering test labs
Despite advances in engineering software, many product validation teams still rely on spreadsheets, shared drives and email
Read more...
Test Planning Best Practices: How TITAN Simplifies Test Plans, Milestones and Coverage
Ask a validation lead in any physical product test lab how their test plan started and you will hear about a spreadsheet.
Read more...
What Are Electronic Lab Notebooks? A Test Lab View
An electronic lab notebook (ELN) replaces the paper notebook used to record experiments, tests, and observations.
Read more...
The Complete Guide to Test Lab Management in 2026
Test labs have become one of the most constrained resources in modern product development. Validation timelines are shrinking
Read more...
A Test Planner's Guide to Hardware Validation
Hardware testing sits at the center of every reliable product program. For test planners, the work goes well past
Read more...
Why Component Suppliers Are Rethinking Test Lifecycle Management
The global automotive material and component testing market reached roughly US$26.91 billion in 2025 and is on track
Read more...
Advantages of using a Unified Testing Platform Over Fragmented Testing Tools
Ask anyone who runs a physical test lab what their week looks like and you will hear a familiar story. The test plan lands
Read more...
The Next 5 Years of Physical Product Testing: A Prediction from the Industry Floor
A product engineer at a mid-size EV components manufacturer spent 14 weeks getting a battery module through
Read more...
How TIC Labs Can Manage Growing Test Volumes Without Losing Operational Control
The Europe Testing, Inspection and Certification (TIC) market is on a sustained growth path. Valued at USD 58.93 billion in 2025
Read more...
The Ultimate Guide to Automotive Crash Testing
Every vehicle on the road today carries the invisible fingerprint of crash testing. Before a single unit reaches a customer,
Read more...
How Leading Chassis and Powertrain Teams Are Closing the Test Traceability Gap
The launch of a dedicated chassis and powertrain testing focus at Vehicle Tech Week North America 2026
Read more...
Premium Wake Boats and the New Rules of Marine Product Testing
Premium watersports boats have become among the most mechanically complex products in recreational manufacturing.
Read more...
What Euro NCAP's 2026 Truck Safety Results Mean for Commercial Vehicle Test Programs
Euro NCAP's 2026 truck safety assessment delivered a landmark result: five out of seven vehicles in the Regional Distribution category
Read more...
A Practical Guide to Choosing and Implementing a Laboratory Information Management System (LIMS)
If you're still running your lab on a combination of spreadsheets, handwritten logs and shared folders with names
Read more...

What -30°C teaches you about a tire
In northern Finland, engineers listen to rubber meet ice in silence so complete it feels deliberate. What they're really chasing consistent
Read more...
When Robots Take the Wheel: What the Bundeswehr's Driverless Testing Shift Means for Modern Test Operations
Germany's Bundeswehr operates the Technical Centre for Land-Based Vehicle Systems (WTD 41) in Trier, a facility whose sole mandate is to ensure
Read more...
5 Questions Every VP of Engineering Should Ask About Their Test Operations
There's a particular kind of silence that falls over a lab when something goes wrong late in the testing cycle. Not the silence of focus or concentration. A heavier kind. The kind that settles
Read more...
Test Data Management: Best Practices for High-Volume Labs
In a high-volume R&D lab, data is everywhere and that's exactly the alarming problem. Test files, equipment logs, video recordings, structured forms, raw observations
Read more...
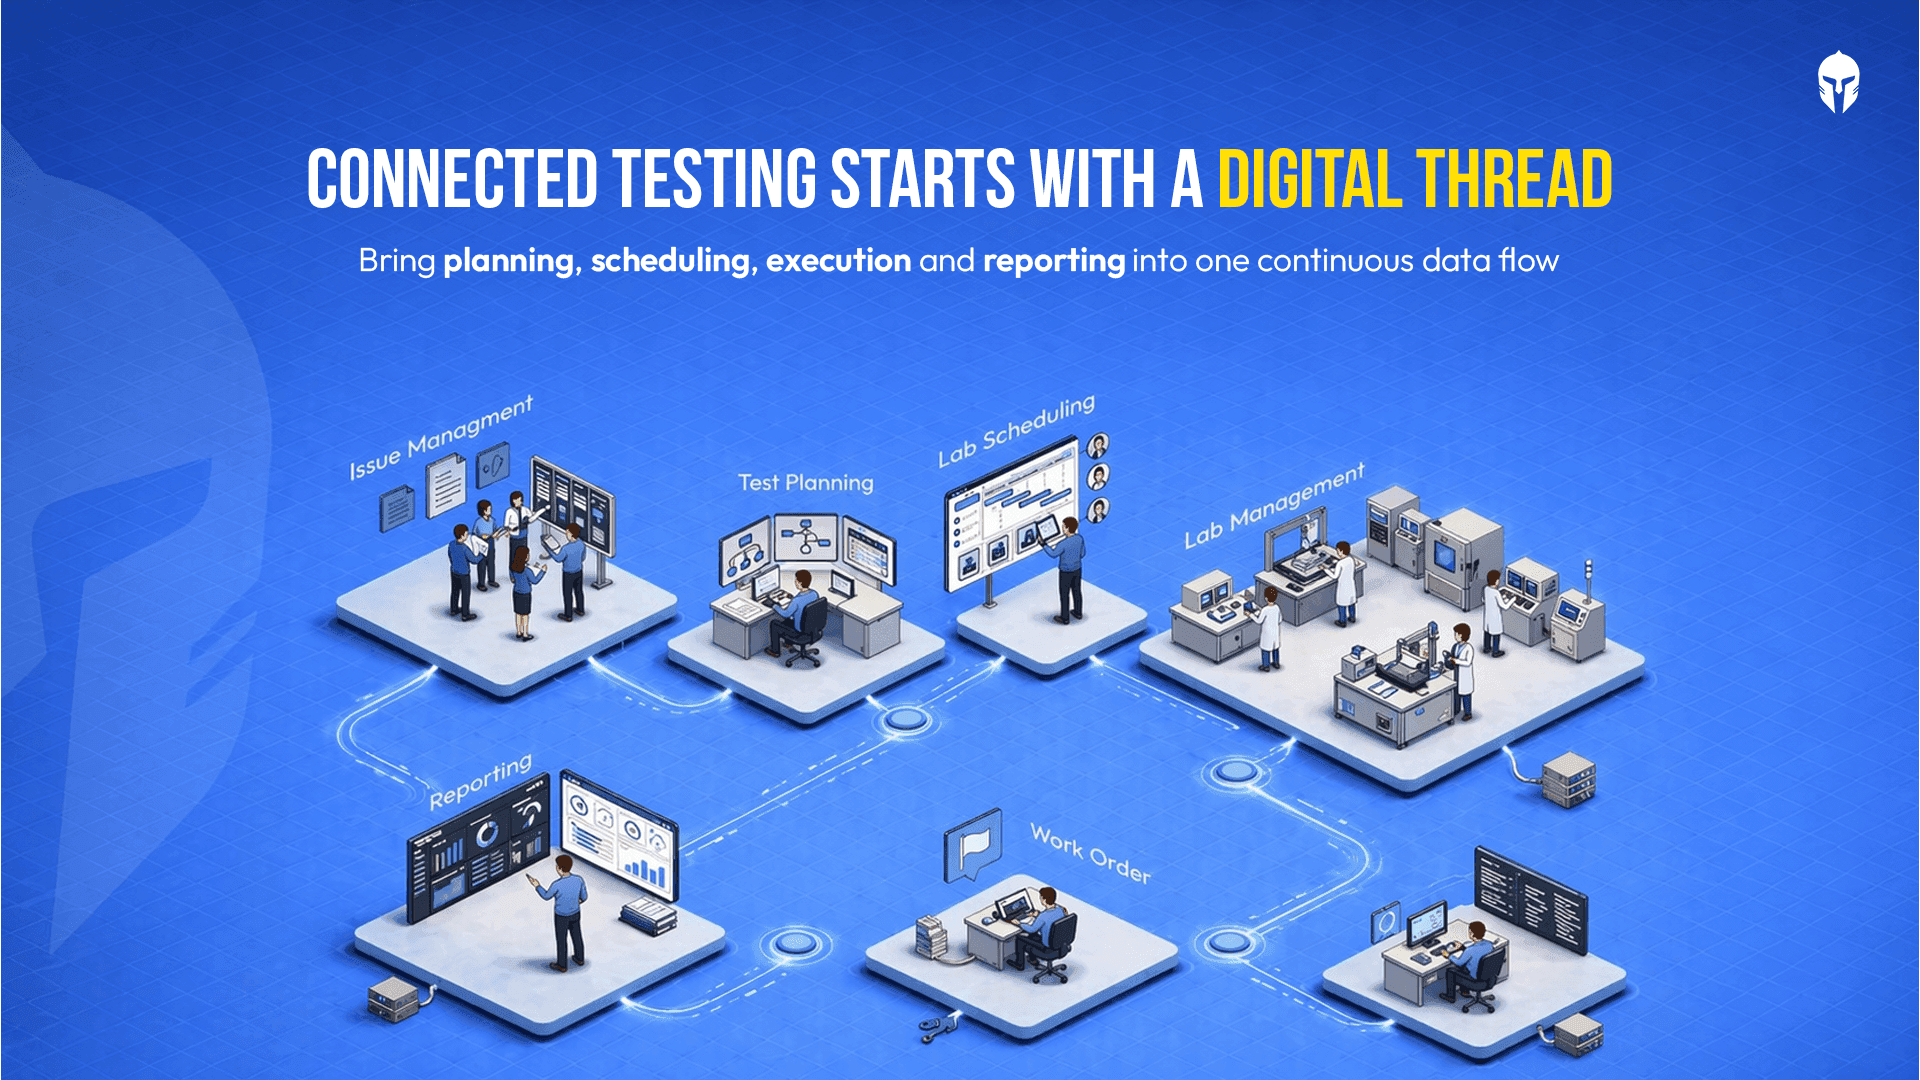
Digital Thread in Physical Product Testing: Hype or Reality?
There is a phrase circulating in engineering circles that sounds almost too good to be true: the digital thread. A single, continuous digital data backbone that connects every phase
Read more...
How Proving Grounds Are Going Digital in 2026
Proving grounds have always been the backbone of vehicle validation. Tracks get booked, prototypes get tested, drivers get scheduled and data gets collected.
Read more...
Paper Records vs. LIMS: Choosing the Right Data Management Strategy for Your Lab
For decades, paper-based record keeping was the backbone of laboratory operations. Binders stacked on shelves, handwritten test logs, manually updated calibration sheets;
Read more...
TITAN as The Inventory Management Platform
Running a modern testing or R&D lab without a reliable inventory management system is like navigating without a map. Equipment runs out mid-experiment. Critical spare
Read more...
AI in Test Scheduling: Six Use Cases Worth Watching
Test scheduling looks administrative from the outside. Inside an engineering lab, it is one of the most layered coordination problems a team faces and one of the
Read more...
What Every Role in Your Test Lab Needs from One Platform
Running a hardware test lab means managing a constant flow of moving parts, schedules, resources, personnel, data or deadlines. When that flow is smooth,
Read more...
Implementing ALCOA in Your Lab: Gaps, Best Practices and What Good Looks Like
In the previous blog, we covered what the ALCOA principles are and why they apply to engineering and testing laboratories every bit as much as they do to pharmaceutical manufacturing.
Read more...

Why ALCOA Is Not Just a Pharma Principle: What Engineering and Testing Laboratories Need to Know
When most professionals hear the term ALCOA, they think of pharmaceutical manufacturing, clinical trials or FDA-regulated environments. That association is understandable, the ALCOA
Read more...
What Is a Design Verification Plan (DVP)? A Practical Guide for Test Engineers
Design Verification Plans (DVP) sit at the heart of any product development program. They define what gets tested, when, how and to what standard.
Read more...
The Test Scheduling Problem Explained
Ask any test engineer what slows down a program and you'll hear the usual answers. Equipment failures. Scope changes. Resource shortages.
Read more...
Home Grown Tools vs TITAN
That internal tool your team built seven years ago. It was genuinely impressive at the time. Someone on the team had a problem; nobody had a budget for a proper solution
Read more...
3 Questions Your Dashboard Should Answer Instantly
There's a framework in operations management that measures any operation across four dimensions - Volume, Variety, Variation and Visibility.
Read more...
How Smart Scheduling Is Beating Million-Dollar Equipment Investments?
You invested heavily in advanced equipment because precision matters. Calibration matters. Speed to market matters. Yet despite those investments,
Read more...
Crash Test Dummies Aren’t Props, They’re Precision Instruments
Step into a contemporary crash testing facility and one thing becomes clear almost immediately.
Read more...
OEM and the Hidden Cost of Fragmentation: Why Test Lifecycle Management Matters?
Picture a weekly sync inside an automotive OEM program, their verification and validation (V&V) teams racking their brains over spreadsheets.
Read more...
How Do You Build ISO/IEC 17025 Ready Labs with End-to-End Digital Traceability?
If you run or work with testing and calibration laboratories whether as an OEM lab, an independent testing facility
Read more...
Any Ambition Bigger Than a Spreadsheet?
Imagine this: It's late on a Friday evening, and Sarah, a dedicated vehicle test engineer at a leading R&D organization,
Read more...
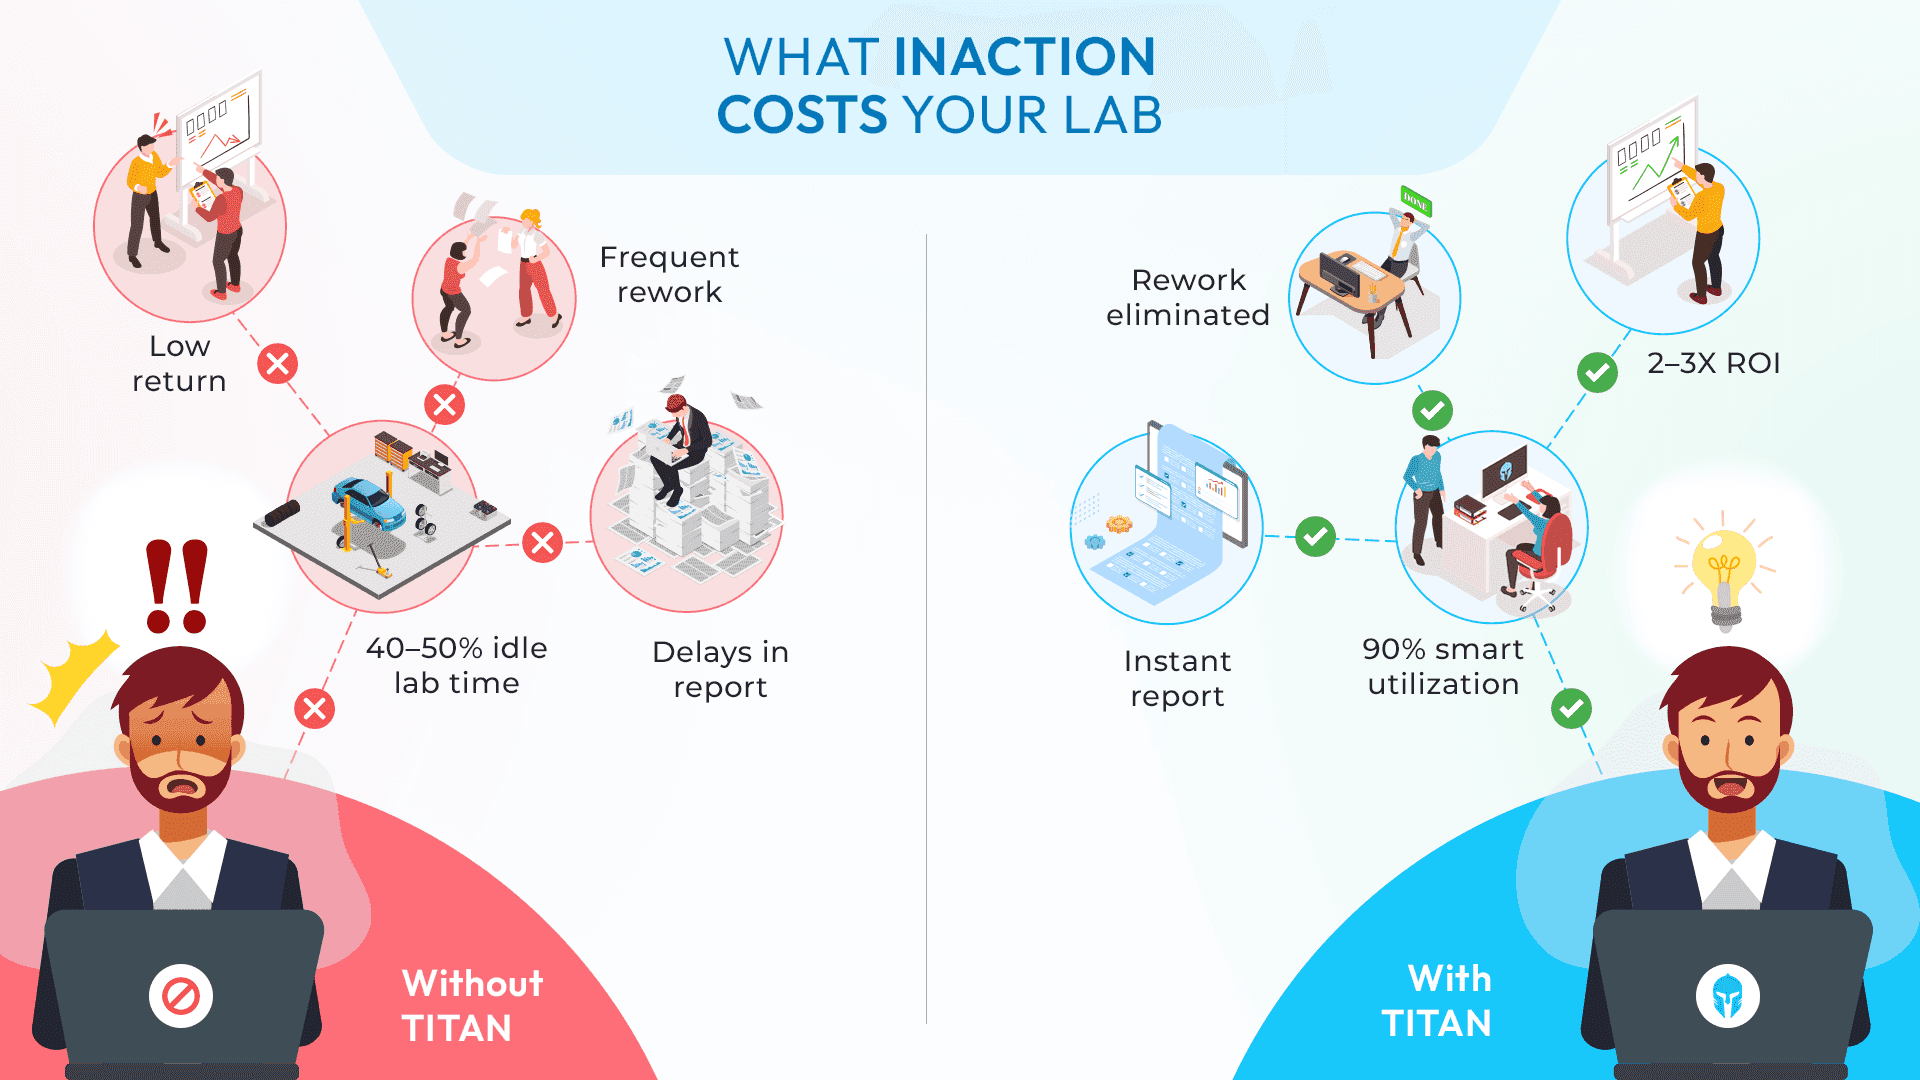
The Cost of Inaction: Why Testing Teams Can't Afford to Delay a Test Lifecycle Management Solution
Many engineering leaders already know their testing teams need a centralized system. The challenge?
Read more...
Best Practices in Lab Asset Management with Titan
Modern laboratories operate under constant pressure: deliver accurate results faster, manage rising costs,
Read more...
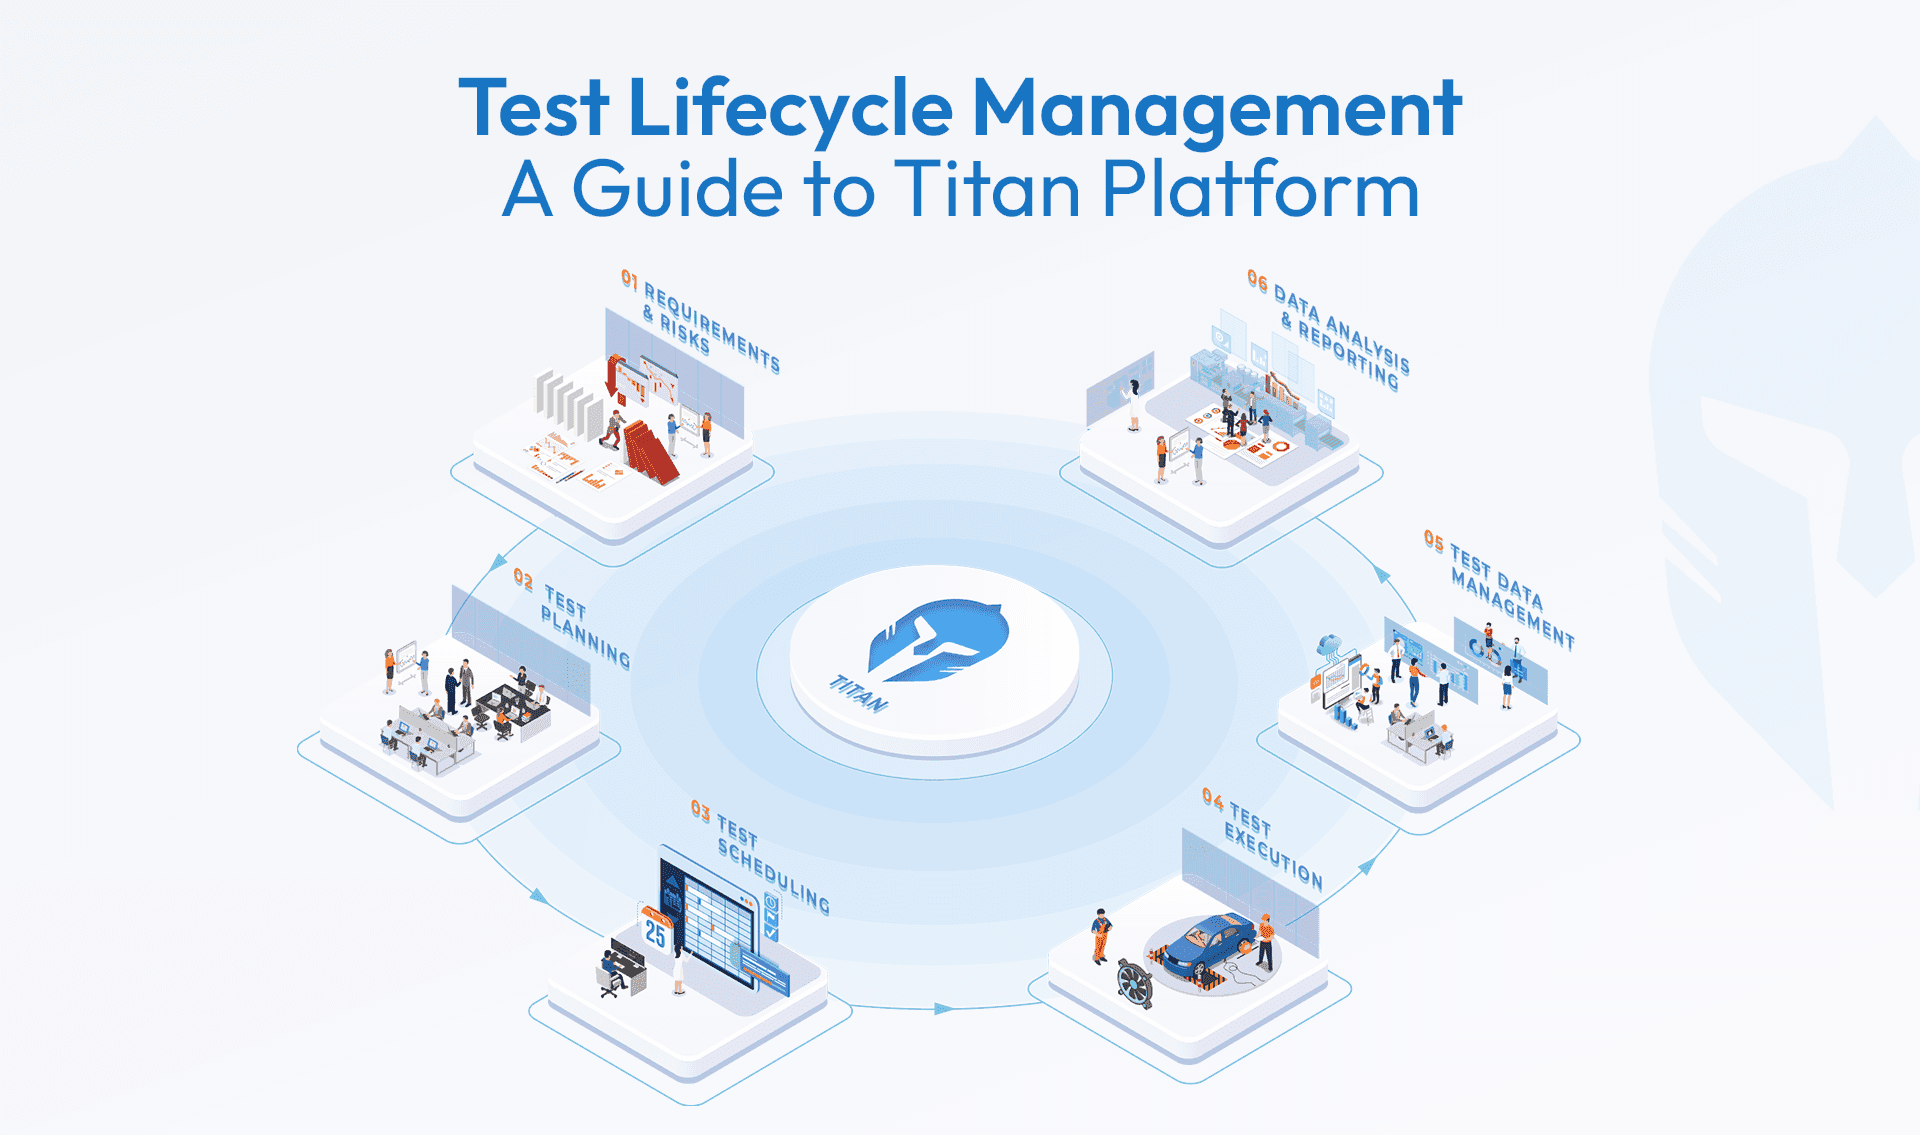
Test Lifecycle Management Explained: What Every Engineering Team Needs to Know
When it comes to product development, testing is more than a box to check it’s the process that validates safety, performance,
Read more...
Can your booking tool do more than just schedule?
Titan's Booking Portal does more than just schedule. It’s a single platform that links test requests,
Read more...
Modernizing Lab Bookings: Email Requests vs. Titan Portal
When managing test labs or proving grounds, it’s common to rely on email threads and manually filled forms from customers
Read more...
Titan for Greenfield OEMs: Managing the Complete Test Lifecycle Beyond Your Walls
Building a product from the ground up as a Greenfield OEM comes with unique challenges.
Read more...
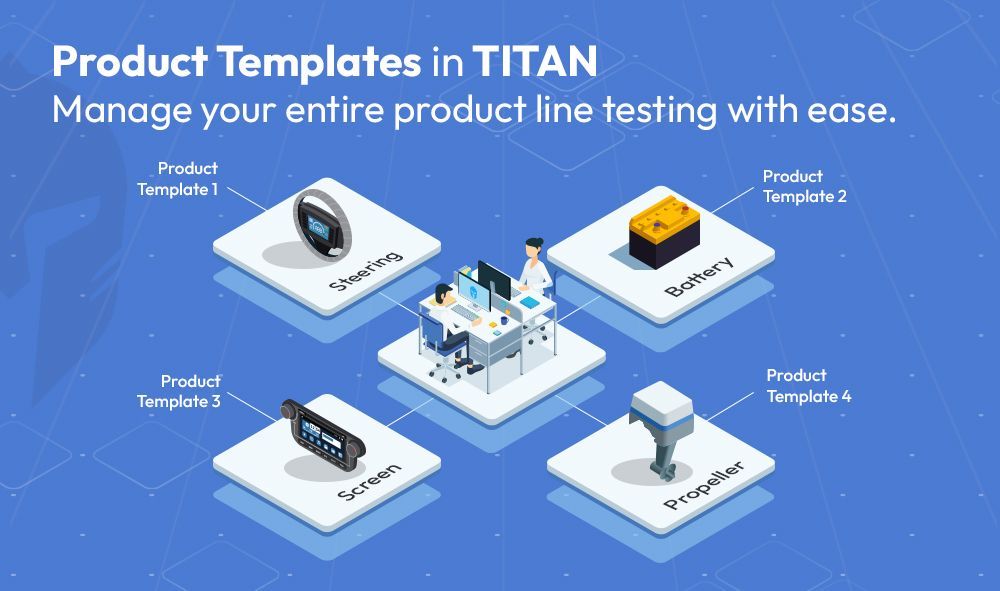
How Titan’s Template-Driven Approach Simplifies Multi-Product Line Test Management
Engineering teams managing diverse product lines often face the challenge of maintaining consistency,
Read more...
How TITAN Supports Laboratories in Achieving ISO/IEC 17025 Compliance
Laboratories across industries are tasked with ensuring the highest standards of testing and calibration.
Read more...
Managing Test Articles Seamlessly with Titan - from Creation to Retirement
In the world of product testing, managing prototype samples and test articles is often a logistical challenge.
Read more...
Rethinking Test Data Governance: How TITAN Powers Compliance, Transparency, and Efficiency
In today’s data-driven testing environment, governance leaders face increasing pressure to ensure compliance
Read more...
Bridging the Scheduling Gap for Modern Test Labs: Why TITAN Is Your Lab's Best Ally
Imagine this: A test lab under constant pressure to meet deadlines is struggling with delays and resource conflicts.
Read more...
From Feedback to Feature: The Addition of Inventory Management in TITAN
Over the years, Titan has evolved by listening closely to the needs and feedback of our customers. As a company that values
Read more...
The Essential Synergy: How a unified Test and Lab Management tool enhances your engineering products’ verification and validation experience?
In the world of engineering product verification and validation (V&V), traceability and efficiency are paramount to giving the earliest green signal for a market launch
Read more...
Streamlining Test Management: Best Practices for Effective Scheduling and Resource Allocation
Efficient management of test requests and scheduling is crucial for any engineering or testing department.
Read more...
Transforming Verification Plan Management with TITAN: Overcoming Traditional Challenges
In today’s fast-paced technological environment, managing verification plans (VPs) with outdated tools like spreadsheets or standalone systems....
Read more...
Streamlining Electronics R&D with TITAN's Advanced Testing Features
In the dynamic world of electronics manufacturing, quality isn’t merely a desirable attribute -- it's critical for achieving market success and maintaining customer trust.
Read more...
Eliminate Productivity Killers with TITAN
Administrative tasks are often the silent killers of productivity, diverting engineering teams from their core mission: driving product improvement,....
Read more...
Maximizing Efficiency in Test Management: The Case for Choosing TITAN Over Custom Solutions
You recognize that streamlining and automating your testing processes will enhance quality while reducing costs. As you consider the idea of creating a....
Read more...
Inventory Management– Never Run Out of Consumable Material Again with TITAN!
In addition to its full end-to-end test management capability, Titan also features a robust Inventory module. Now you can manage all the consumable items that....
Read more...
Preventive Maintenance – Another Great Feature from TITAN!
A testing team understands that it is only as good as its equipment. If equipment is neglected -- or maintained incorrectly -- the organization is at risk,....
Read more...
TITAN: An Engineer’s Ally
Greetings fellow engineers, we're excited to introduce your new ally, dedicated to your work satisfaction. Over the years, we have had meetings and discussions ....
Read more...
Standardization: Engineering Testing Should Be Standardized, too!
Engineering and IT executives are continually on the hook to deliver savings while streamlining processes and improving quality....
Read more...
Meeting the Crash Testing Challenge
You get one chance to get a crash test right. There are no do overs. You need to ensure every step has been followed meticulously, checked and double checked....
Read more...
DVP Essentials: How TITAN Guarantees Comprehensive Test Coverage with Enhanced Product Quality
In today's fast-paced manufacturing landscape, product success relies on robust design and validation processes. Rushing products to market can lead to....
Read more...
Standardization of Testing Practices – How TITAN Makes It Happen!
Enforcing corporate-wide standardization is a challenge. Over the course of doing business, each engineering department has developed specific testing processes....
Read more...
How TITAN provides Flexibility and Configuration Options for your Unique Workflows ?
When it comes to testing, every organization has its own distinct processes, workflows, and requirements. One-size-fits-all solutions often fall short of....
Read more...
I love making reports. Said NO ENGINEER. EVER.
Every engineer procrastinates preparing a test report as the efforts are high and it consumes lot of his engineering hours. Having said that, test reports remain critical....
Read more...
Challenges in Autonomous Vehicle Testing and Validation
A study, prepared by Strategy Analytics, predicts autonomous vehicles will create a massive economic opportunity that will scale from $800 billion in 2035....
Read more...
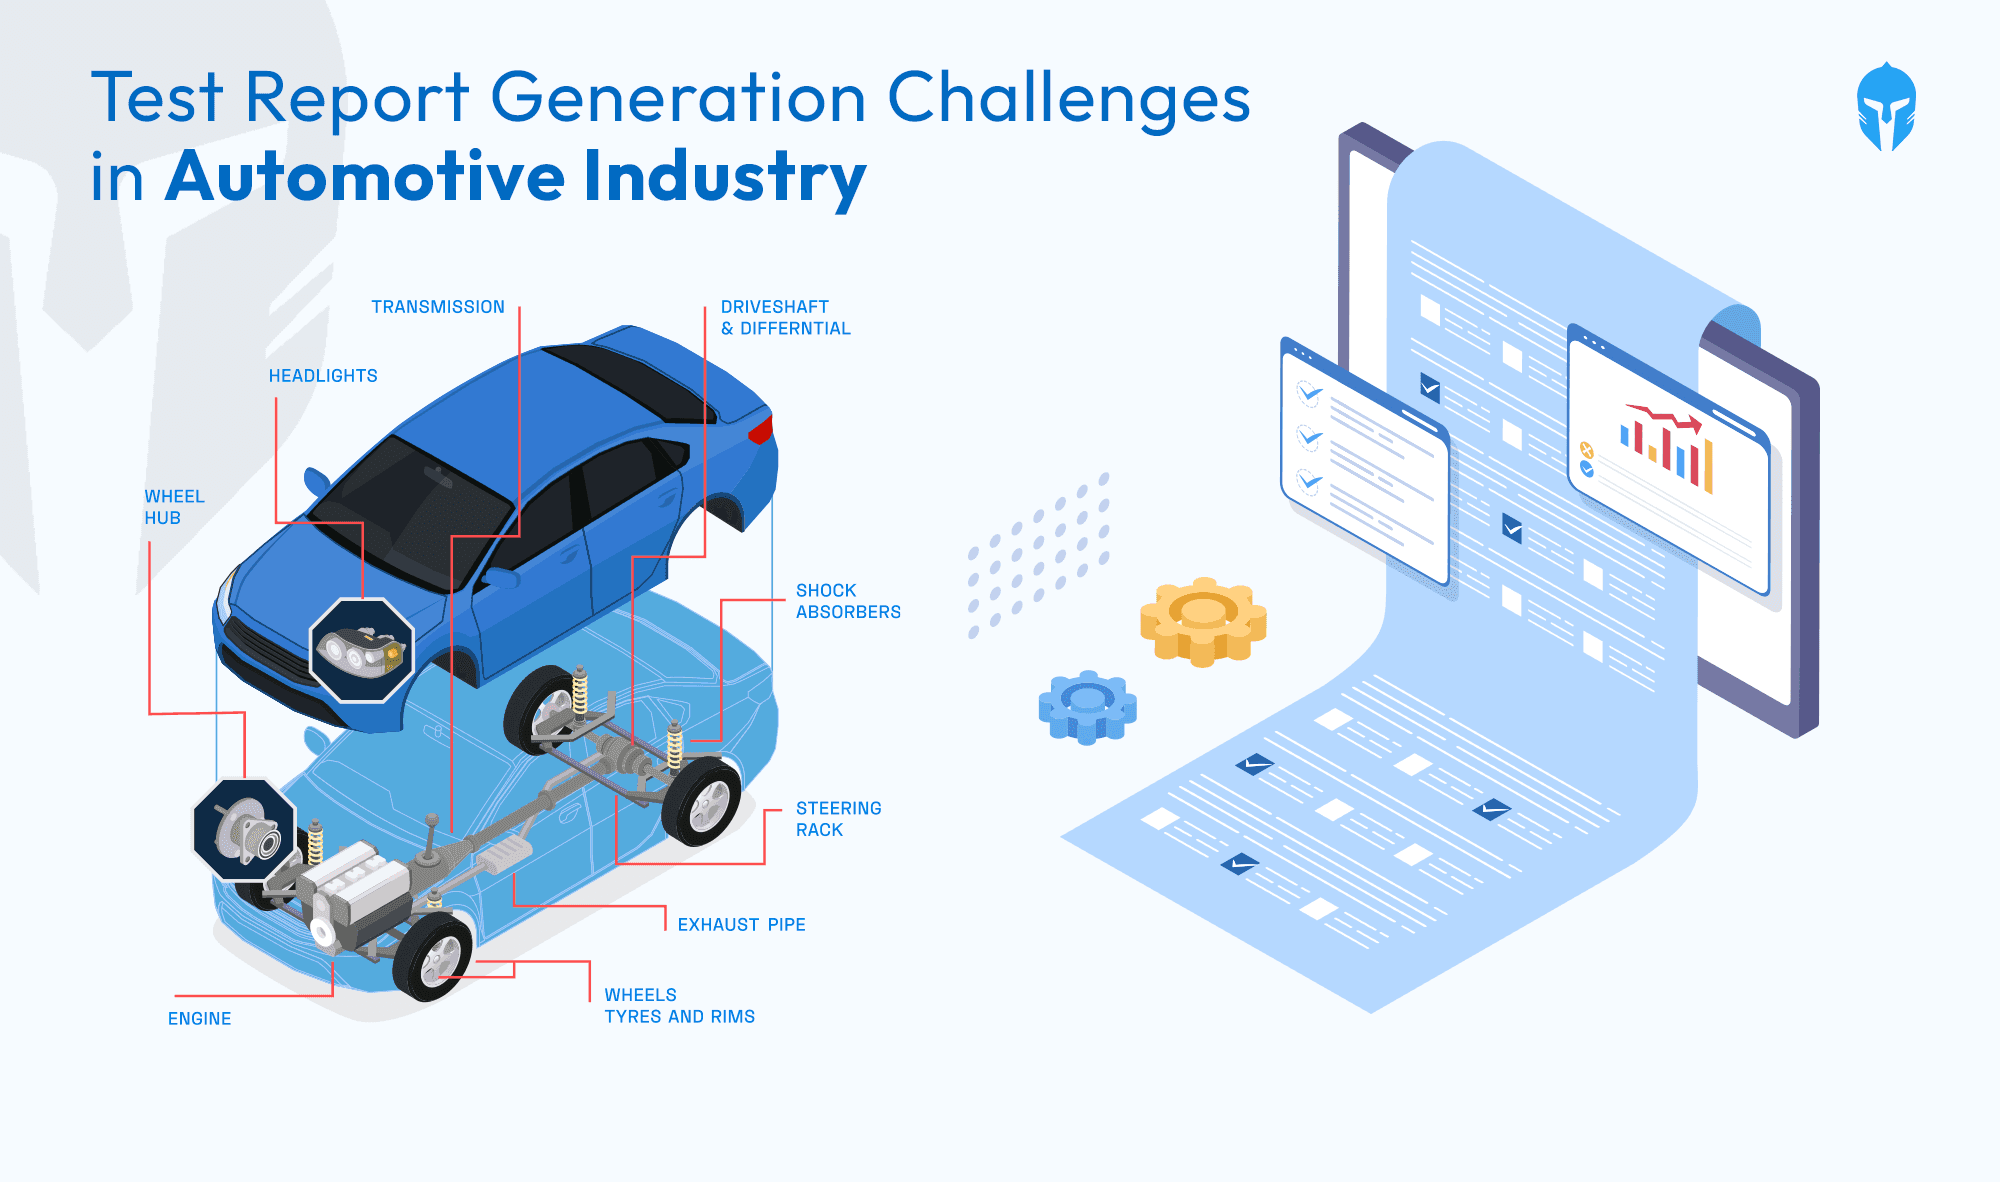
Test Report Generation Challenges In Automotive Industry
Ever wondered how the wheels of vehicle development keep turning smoothly? In the fast-paced realm of vehicle development, where informed decisions....
Read more...

Need For Prototype Vehicle Management System
Prototype testing has been around for as long as humans have been inventing. Creating the best version of a tool requires trial and error, and without testing,...
Read more...
A Complete Guide: Crash Testing For Automobile
A Complete Guide: Crash Testing For Automobile Road accidents are the major cause of death worldwide, even after strict rules and heavy...
Read more...
How To Manage End-To-End Vehicle Test Process
How To Manage End-To-End Vehicle Test Process Testing Beyond Boundaries With TITAN TITAN has established itself as a leader in vehicle...
Read more...
Test Incident & Concerns Management
Test Incident & Concerns Management In developing any new product, you invest a great deal of time and energy into testing your products...
Read more...
Why do you need Test Lifecycle Management
Why do you need Test Lifecycle Management We’re living in a time period where we have integrated software tools and apps into every...
Read more...